AI SoftwareCorporation

Server-Side & APIsServer-Side & API Development

APIs and services that stay fast, secure and easy to change

We build the server side your products depend on: APIs, services, integrations, data models and background jobs.

Seen from behind, two developers at a desk review code on a laptop, a large monitor behind it.

Outcomes

Stable contracts, safe integrations

  • Contracts other teams can build on

    APIs are specified first in OpenAPI or a GraphQL schema, so web, mobile and partner teams can build in parallel against mocks instead of waiting for the back end.

  • Peak behavior known in advance

    Load tests and query-⁠plan reviews run against the targets you set before launch, so you see how the system behaves at peak ahead of your busiest day.

  • Security that doesn’t wait for launch

    Authentication, authorization, input validation and secrets handling follow OWASP guidance and are checked in the pipeline, not in a review the week before launch.

  • Integrations that fail safely

    Retries, idempotency keys and dead-⁠letter queues mean a partner outage delays data instead of losing or duplicating it, and someone is alerted when a sync stalls.

Capabilities

APIs, integrations and the data behind them

We work in Node.js, Python, Java, .NET and Go, and choose the language and architecture your own team can run and extend after handover.

API design and development

REST, GraphQL and gRPC APIs shaped around the clients that call them, specified before they are built, and versioned so breaking changes arrive with notice.

  • Contract-⁠first design in OpenAPI or GraphQL
  • Consistent errors, pagination and idempotent writes
  • Versioning and deprecation policies consumers can plan for
  • API gateways, rate limits and usage analytics

Architecture and modernization

We choose the simplest architecture your team and load call for, often a modular monolith, and modernize legacy back ends one capability at a time, without a big-⁠bang rewrite.

  • Service boundaries drawn with domain-⁠driven design
  • Modular monoliths with enforced module boundaries
  • Strangler fig migration off legacy back ends
  • Technical debt ranked by impact, then paid down

Integration with ERPs, CRMs and partners

ERP, CRM, payment and partner systems exchange data through well-⁠defined interfaces, with one source of truth per record and an alert when a sync fails.

  • APIs, webhooks, message queues and file feeds
  • Change data capture where timing matters
  • Field mapping, validation and reconciliation reports
  • Replay tools for failed or partial syncs

Events, messaging and background work

Work that shouldn’t hold up a user request runs on queues and event streams: imports, notifications, and calls to slow third-⁠party services or AI models.

  • Kafka, RabbitMQ or managed cloud queues
  • Transactional outbox for reliable event publishing
  • Idempotent consumers, retries and dead-⁠letter queues
  • Scheduled jobs with visible status and history

Data modeling and performance

Schemas follow how data is written, read and retained. Performance is tuned from evidence, such as query plans, profiles and load tests, against the targets you set.

  • Relational or document models, chosen per workload
  • Zero-⁠downtime migrations using expand and contract
  • Indexing, query tuning and caching with Redis
  • Stateless services that scale horizontally

Security by design

Threats are modeled while the design is still on paper. Controls are then checked on every pull request and tested before release against OWASP guidance and your policies.

  • OpenID Connect sign-⁠in and OAuth 2.0 API access
  • Role-⁠ and attribute-⁠based authorization checks
  • Secrets in a vault, never in code
  • Threat modeling and OWASP ASVS verification

Approach

Contracts first, then thin, tested slices

  1. Step 1: Map the domain and constraints

    We learn the business rules, the systems involved and the limits on load, latency, availability and data handling before choosing an architecture.

    Activities

    • Domain workshops with product and operations teams
    • Review of existing code, data and integrations
    • Non-⁠functional requirements agreed and written down

    You receive

    • Context map of domains, systems and data owners
    • Non-⁠functional requirements and open risks
  2. Step 2: Design contracts and architecture

    APIs, events and data models are specified before implementation, so the teams that depend on them can review them early and build against mocks.

    Activities

    • OpenAPI, GraphQL or AsyncAPI contracts reviewed with consumers
    • Threat model of trust boundaries and sensitive data
    • Architecture decisions recorded with their trade-⁠offs

    You receive

    • Versioned API and event contracts
    • Architecture decision records
  3. Step 3: Build in thin, tested slices

    Each slice runs end to end, from API to database, behind automated tests and a CI/CD pipeline, and is demonstrated as working software.

    Activities

    • Unit, integration and consumer-⁠driven contract tests
    • Code review, static analysis and dependency scanning on every pull request
    • Feature flags for work that isn’t ready for users

    You receive

    • Working, tested services in your repositories
  4. Step 4: Harden for production

    Before launch we load-⁠test with realistic traffic, verify the security controls and make sure every service reports its own health.

    Activities

    • Load, stress and soak tests against agreed targets
    • Security testing against OWASP ASVS requirements
    • OpenTelemetry traces, metrics and structured logs

    You receive

    • Load-⁠test results and tuning notes
    • Dashboards, alerts and runbooks for each service
  5. Step 5: Release and hand over

    Changes roll out gradually with a tested rollback path. Your team then takes ownership through pairing and documentation, or we stay on to extend and support the system.

    Activities

    • Canary or blue-⁠green releases with monitoring
    • Pairing and architecture walkthroughs with your engineers

    You receive

    • A system your team can run, change and extend

Deliverables and fit

Code, contracts and tests you own

What you receive

8 deliverables
  • Context map, non-⁠functional requirements and target architecture
  • Versioned API and event contracts with generated reference docs
  • Source code in your repositories, with unit, integration and contract tests
  • Database schemas with tested, reversible migration scripts
  • CI/CD pipeline with static analysis and dependency scanning
  • Threat model and security test findings, with fixes applied
  • Load-⁠test scripts, results and capacity notes
  • Dashboards, alerts, runbooks and architecture decision records
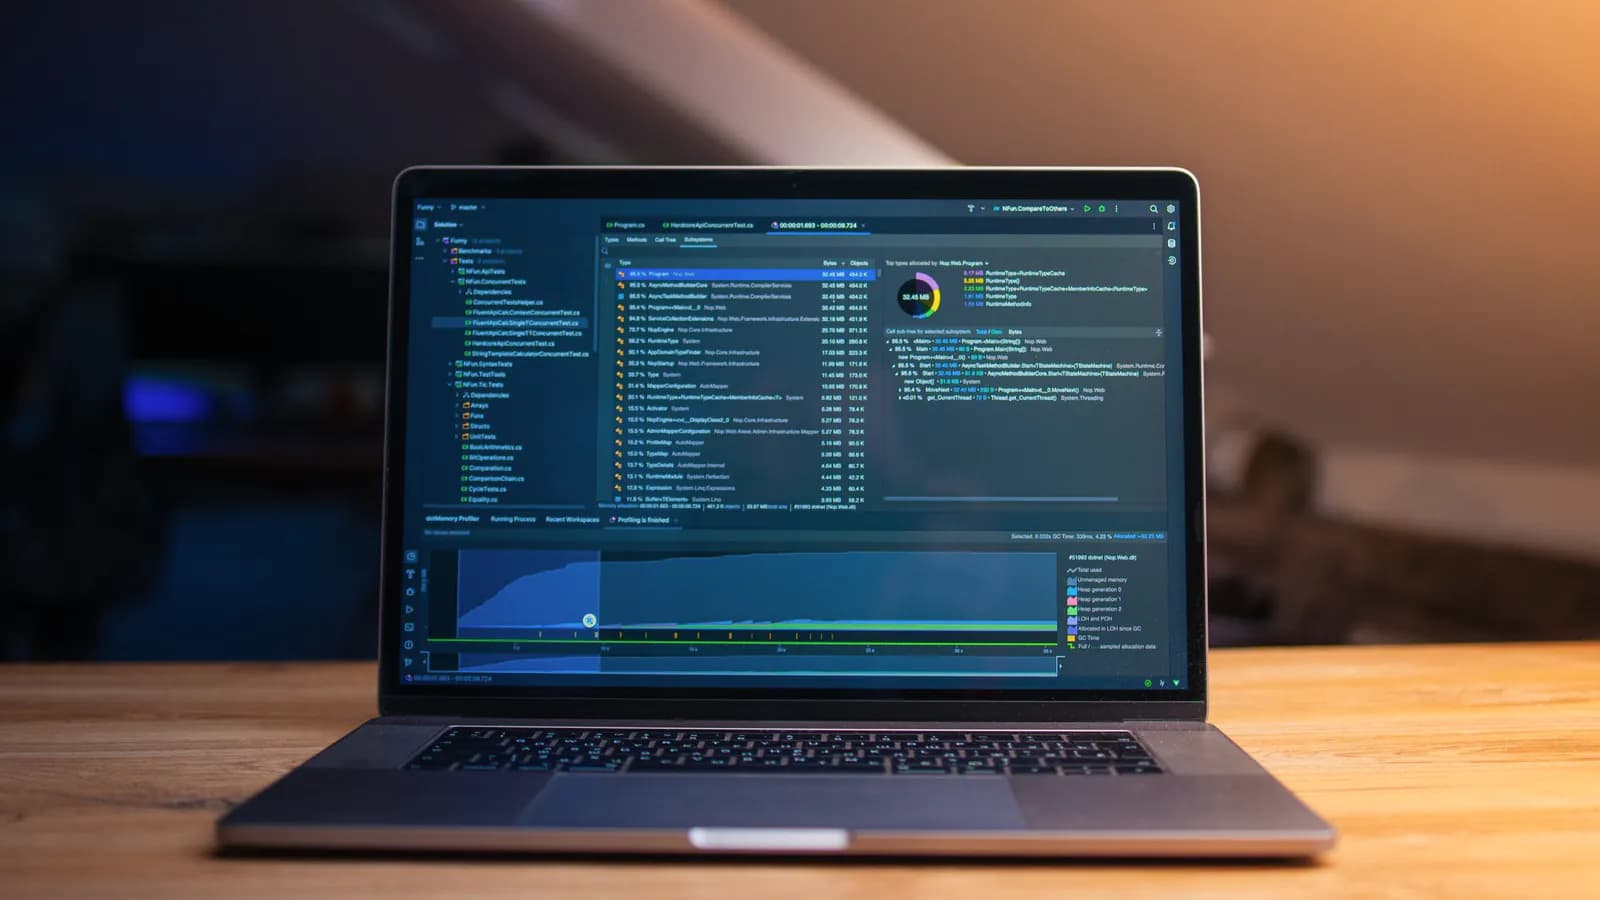
An open laptop on a wooden desk shows a performance profile: a list of calls above a timeline chart.
Performance checked against your targets before launch

A good fit if

  • Web, mobile or partner teams are waiting on APIs you don’t have yet
  • Staff copy records between your ERP, CRM and other tools by hand
  • Your back end slows down or times out at peak, and the cause is still a guess
  • Changing the monolith feels dangerous, and replacing it outright isn’t feasible
  • Security reviews keep finding the same access-⁠control or data-⁠exposure issues
  • You’re starting a new product and want a back end designed to grow with it

Engagement models

One API, a whole back end or extra engineers

The models that usually suit this service. You can switch as the work changes.

  • Project delivery

    A single API or integration, or a new back end, with the contract agreed first.

  • Dedicated team

    A long-lived product back end, developed by a team that keeps its context.

  • Team extension

    Senior server-side engineers joining your team for a deadline or a migration.

Technology

Languages and data stores

Listed so you can check the fit with your stack. None of them implies a partnership or certification.

Tools and platforms

  • Node.js
  • TypeScript
  • Python
  • Java
  • Kotlin
  • Spring Boot
  • Go
  • .NET
  • GraphQL
  • OpenAPI
  • Apache Kafka
  • RabbitMQ
  • PostgreSQL
  • Redis

Illustrative scenario

Illustrative scenarioCarving a booking API out of a freight monolithRead the scenarioHide the scenario
Illustrative scenario

Carving a booking API out of a freight monolith

A freight forwarder whose quoting, booking, tracking and invoicing all run inside one aging application.

Challenge
Releases are rare and risky, the people who wrote the core now work elsewhere, and key customers want to book shipments through an API instead of by email.
Approach
  1. 1Cover the busiest booking paths with characterization tests before changing any code
  2. 2Agree on an OpenAPI contract with pilot customers and give them a sandbox with mock responses while the service is built
  3. 3Put a routing layer in front of the monolith so booking traffic can move over one capability at a time
  4. 4Build the booking service with OAuth client credentials and per-⁠customer rate limits, publishing booking events through a transactional outbox so tracking and invoicing stay in sync
  5. 5Switch off the legacy booking code once no traffic reaches it
Outcome
Customers book through a documented, secured API rather than by email, operations keep running throughout, and the monolith shrinks slice by slice with no single high-⁠risk cutover.
Ask about a project like this

FAQ

Questions about APIs and integrations

Ask a question

Should we build microservices or a monolith?

Most systems are best started as a modular monolith: one deployable application with strict boundaries between its modules, which is simpler to run, test and change. We split a module out into its own service when it needs to scale, release or be owned independently. Boundaries drawn early make that split straightforward when the time comes.

Which languages and frameworks do you work in?

We work in Node.js and TypeScript, Python, Java and Kotlin, .NET and Go, with PostgreSQL and other mainstream databases. If you have an established stack, we work in it, because your team will maintain the code. For a new system we recommend a stack based on your team’s skills, the workload and the people you can hire, and set out the trade-⁠offs in writing.

Can you build a single API or integration rather than a whole platform?

Yes, and a well-⁠bounded integration is often a sensible place to start. We agree on the contract first, document it with OpenAPI, and build in authentication, versioning, monitoring and failure handling so it holds up once other teams depend on it.

Do we have to rewrite our legacy back end?

Rarely. We usually put a routing layer in front of the existing system, rebuild capabilities one at a time and move traffic across once each one proves itself. Both versions operate in parallel, so the business keeps running and every step can be reversed.

Can you connect AI features to our existing systems?

Yes. The back end is where an AI feature meets your real data and permissions, so we treat model calls like any other external dependency: behind your own API, with authentication, rate limits, timeouts, queues for slow requests and logs that leave out sensitive fields. Prompt design, retrieval and evaluation are covered by our Generative AI & LLM Solutions service, and we plan both together.

Next step

Which API or integration comes first?

Describe the system, process or decision in front of you. Expect questions back, a sensible first step and a fitting engagement model.

First step
A conversation about the problem, your systems and constraints
You leave with
A view on whether we can help, and a sensible first step
Before any work
A written proposal covering scope, team, approach and terms
Commitment
None until you approve that proposal